Cybersecurity services · Arlington, Virginia

Who owns your cybersecurity?

A fractional CISO does, for businesses in Northern Virginia and DC.

Answer six quick questions

30 minutes. A written scope before you commit.

What usually prompts the call

Most engagements start with one of these four moments. Each one has a concrete first step.

  • An insurance renewal

    The carrier's questionnaire asks about controls nobody can confirm.

    We confirm what is in place and document the evidence behind each answer.

  • A client security review

    A larger client sends a security questionnaire, and a contract waits on the answers.

    We help you answer accurately, with the documentation to back it up.

  • A board or investor question

    Someone asks who owns cyber risk, and there is no clear answer.

    An executive risk briefing, and a named owner from then on.

  • An incident or near miss

    A compromised mailbox, a fraudulent invoice, a lost laptop.

    Call 202-909-8237. We help you contain it, then close the gap it came through.

Security leadership, applied to everything you run

We lead your security program, then hold your AI tools and your website to the same standard. You can start with any one of them.

Cybersecurity

Someone has to own your security: set the standard, check the work, and answer to your board, your insurer and your clients. We take that job, whether you have an IT team, an outside provider or nobody yet.
An open report titled Executive risk briefing with three numbered priorities and a fountain pen, lit by a warm light at night
From a security briefingExample
  • Email account takeoverOwner: operations lead · due week 2High
  • Backups never test-restoredOwner: office manager · due week 3High
  • Former staff still have accessOwner: HR lead · due week 1 · quick winMedium
Read a full example briefing
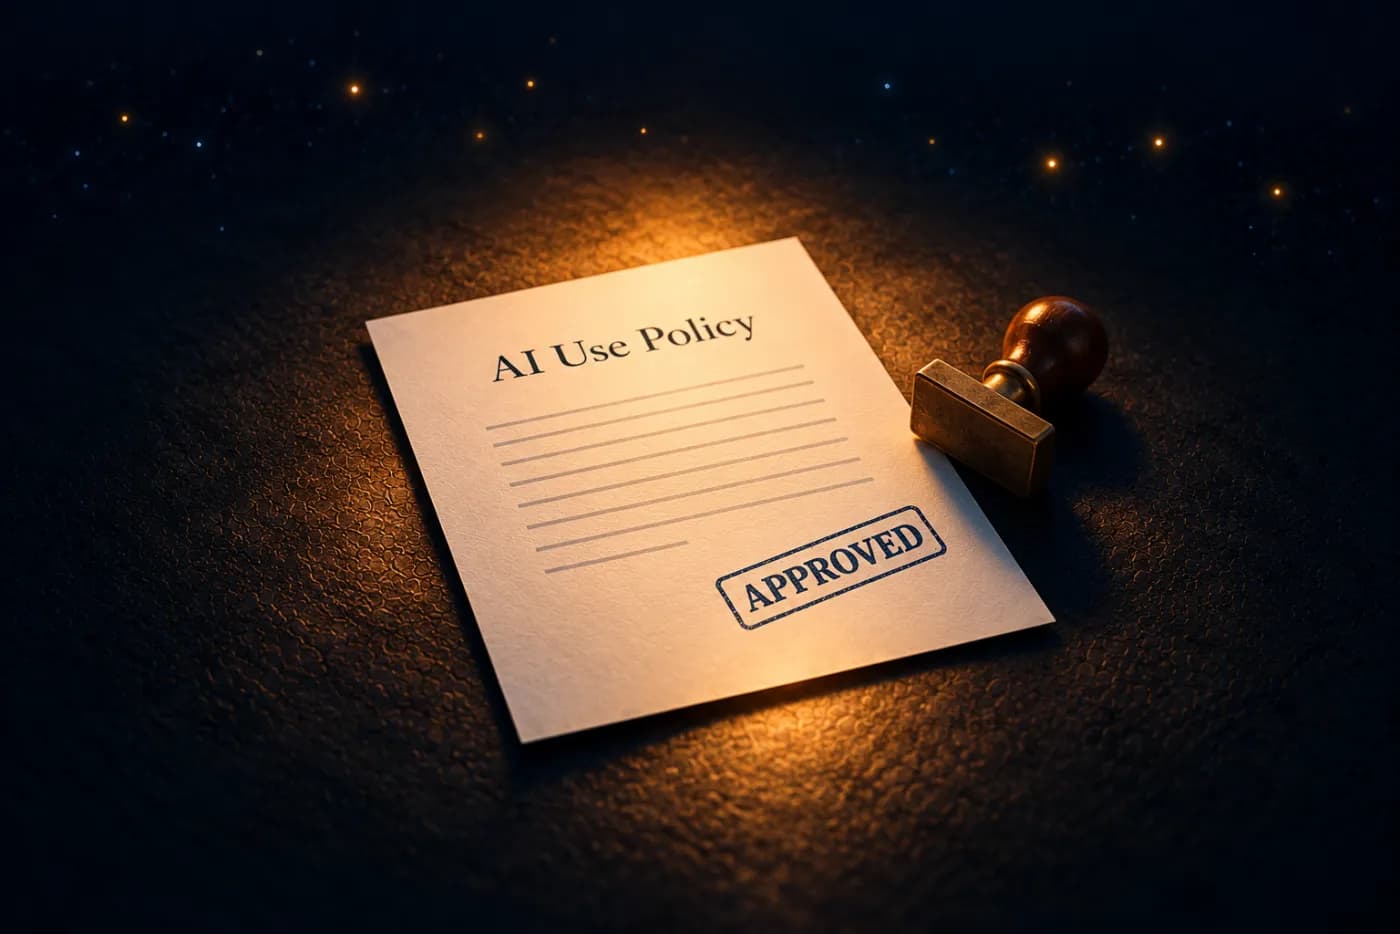
An AI Use Policy document stamped Approved, with a desk stamp beside it
From an AI use policyExample
  • Client dataNever entered into AI tools
  • Internal documentsCompany-approved assistant only
  • A new AI toolApproved by the policy owner before use

Web design

Your website is the first thing a client checks and an easy way in for an attacker. We design and build it with security checked before launch, then host and maintain it.

A laptop showing the NightFortress website, with a brass padlock in front of it
From a launch checklistExample
  • Encryption and security headersChecked before launch
  • Contact formsProtected from spam and abuse
  • BackupsDaily, stored off-site, restore tested

Six questions every business should be able to answer

Security work needs a clear owner. These questions help identify what to verify. Your answers stay on this page.

Question 1 of 6 · Ownership

Can you name the person accountable for your cybersecurity?

How working with us starts

You see the scope in writing before you commit. Urgent risks are handled first, whatever the plan says.

  1. Tell us what prompted the call

    A renewal, a client questionnaire, an incident, or a sense that nobody owns this. Request a consultation and we'll arrange a time.

  2. Talk it through

    A 30-minute conversation with a senior security lead about your situation. If you'd like to prepare, the free cybersecurity assessment is optional.

  3. Get a written scope

    Deliverables, timeline and terms in writing, before you commit to anything.

An example: the first 90 days with a fractional CISO

  1. Weeks 1 to 2

    Baseline and priorities

    Accounts, devices, vendors and exposure mapped, and the urgent risks named.

  2. Weeks 3 to 4

    Roadmap and briefing

    A 90-day plan and an executive briefing, in plain language.

  3. Months 2 to 3

    Policies and fixes

    Policies written, top fixes moving, oversight in place.

  4. Ongoing

    Monthly reporting

    Roadmap ownership, reporting and incident leadership.

Whoever runs your IT, someone should judge whether it is safe

Keeping technology running and owning its risk are different jobs. Your IT may be run by you, one member of staff, a team or an outside provider. Someone still has to set the security standard, check the work against it and report to you on it, and the people who run it shouldn’t be the only ones checking it. That is the job we take. When we build something for you, such as a website or an automation, we hold it to the same written standard and show you the evidence.

  • Not a managed IT providerWe don't run a help desk, manage devices or sell hardware. If someone else runs your IT, we work alongside them.
  • Not an auditor or certifierWe prepare you for audits, questionnaires and assessments. We don't sign them off.
  • Not a 24/7 monitoring centerIf you need round-the-clock monitoring, we help you choose it and hold the provider to account.

Questions buyers ask first

More in the full FAQ

What is a fractional CISO?

A part-time chief information security officer: the senior person who owns your security program, sets priorities and reports to leadership, on a monthly retainer instead of a full-time salary. You may also hear it called a virtual CISO, or vCISO.

Do we need an IT department to work with you?

No. Some clients have an IT team or an outside provider, some have one person who handles it, and some have nobody yet. We work with whatever you have. If someone else runs your IT, we work alongside them.

What does it cost?

Every engagement is scoped to the company, so we don't publish prices. What moves the effort: your size and the systems you run, the obligations you carry to insurers, clients and regulators, what is already in place, and how hands-on you need us to be. After a consultation you receive a written scope with the deliverables, timeline and terms before you commit.

How quickly can we start?

Most engagements begin within two weeks of the first call. An assessment can start within days.

Where do you work?

We're based in Arlington, Virginia, and work with businesses across Northern Virginia and Washington, DC. Much of the work is remote, with on-site sessions across the region.

Start with a conversation

A 30-minute call about your situation, then a written scope before you commit to anything.

See how we work

Urgent concern? Call 202-909-8237